A practical investigation into cookies, browser fingerprinting, first-party data, privacy APIs and the new surveillance economy
For years, the internet had a remarkably simple trick for remembering you.
You visited Website A. Somewhere inside the page, a tiny piece of information was stored in your browser. Later, you visited Website B. An advertising company embedded in that page could recognise the same browser.
You did not have to introduce yourself.
The browser did it for you.
That was the power of the third-party cookie.
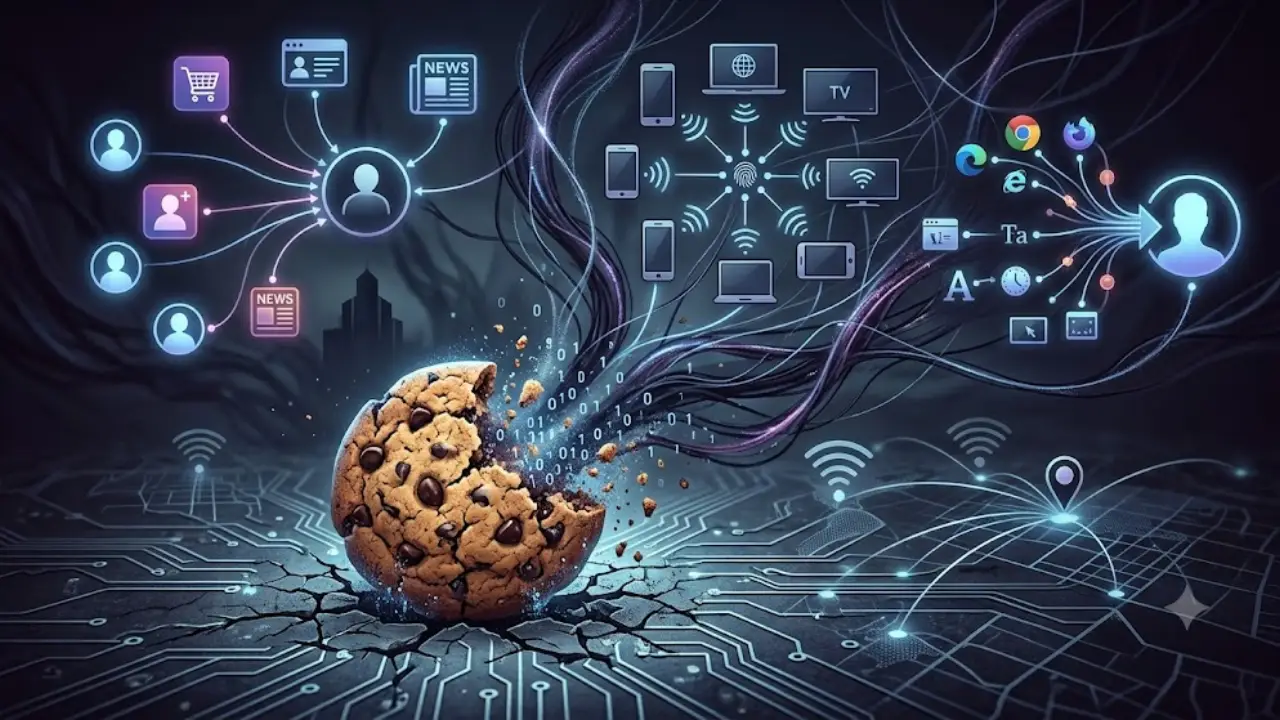
It helped build the modern advertising machine because it allowed companies to connect pieces of behaviour scattered across otherwise unrelated websites. A product viewed on one site could become an advertisement on another. An advertising network could measure whether an impression eventually became a purchase. A company could construct an increasingly detailed picture of a person’s interests.
But the cookie itself was never the whole surveillance system.
And that distinction matters enormously today.
Google announced in April 2025 that Chrome would not introduce a new standalone prompt forcing users to decide whether to retain third-party cookies, and would instead maintain its existing approach to user choice. The UK Competition and Markets Authority subsequently released Google’s earlier Privacy Sandbox commitments. In other words, the famous “death of the third-party cookie” has become much less literal than many headlines suggested.
Meanwhile, Safari and Firefox have taken much harder approaches to cross-site tracking.
So the real story is not simply:
Cookies are dying.
It is:
The internet is moving from one universal tracking mechanism toward a fragmented battle between browsers, advertisers, publishers, platforms and increasingly sophisticated identification systems.
And that changes what privacy means.
First, What Exactly Is a Third-Party Cookie?
A cookie is simply a small piece of data associated with a website.
A first-party cookie belongs to the site you are visiting.
For example:
news.example.com → its own cookie → remembers your login or preferences
A third-party cookie belongs to a different domain embedded within the page.
Imagine visiting:
news.example.com
The page contains an advertising system operated by:
ad-company.example
That advertising company can potentially place or read information associated with its own domain while appearing across thousands of other websites.
That is where the tracking power emerged.
The browser effectively became a meeting place where an advertising company could recognise the same browser in different contexts.
Third-party cookies were therefore useful for:
behavioural advertising;
frequency capping;
retargeting;
cross-site analytics;
advertising attribution;
audience segmentation;
recognising returning users;
synchronising identifiers between advertising companies.
MDN notes that third-party cookies have historically been used for everything from embedded login systems to analytics, personalised advertising and cross-site interest measurement.
The important distinction is this:
A cookie is storage. Tracking is a system.
Destroying one storage mechanism does not automatically destroy the system.
The Five Technologies You Should Not Confuse
| Technology | What it does | Can it track across sites? | Main privacy concern |
| First-party cookie | Stores information for the site you’re visiting | Sometimes, through other mechanisms | Site knows your behaviour |
| Third-party cookie | Allows an embedded third party to recognise you across sites | Yes, traditionally | Cross-site profiling |
| Tracking pixel | Sends a request when an image/script/content loads | Yes, if combined with identifiers | Invisible behavioural measurement |
| Browser fingerprint | Uses browser/device characteristics to recognise a device | Potentially | Harder to see or delete |
| Logged-in tracking | Uses an account identity to connect behaviour | Yes, often across services owned by one company | Identity becomes the identifier |
A tracking pixel is particularly easy to misunderstand.
It does not have to be a literal visible “pixel”.
It can be an invisible request triggered when a page loads. WebKit describes the classic advertising model in which a tracking pixel could report activity from a destination website back to an advertising platform that recognised the user through a cookie.
The US Federal Trade Commission similarly warns that websites and apps can use cookies, pixels, fingerprinting and other mechanisms to identify or follow users.
And then there is the login.
Suppose you are logged into a giant technology platform.
The company may not need a third-party cookie to know that you visited a website containing one of its services.
The identity already exists on its servers.
This is one reason the phrase “cookie-free” can be dangerously comforting.
What Happens When Third-Party Cookies Disappear?
Imagine an advertising company that previously knew:
User 7812
visited:
a news website;
a travel website;
a shoe retailer;
a financial website;
a recipe website.
Without the cross-site identifier, those visits become much harder to join together.
That is good for privacy.
But advertising still needs to answer a commercial question:
Did the advertisement work?
Publishers need to answer another:
Who is interested in our content, and how much should advertising space be worth?
And advertisers ask:
Which audience should receive this advertisement?
The industry therefore began looking for alternatives.
Some are genuinely privacy-preserving.
Others simply move the identity problem somewhere else.
The Replacement Strategy: Stop Following the Person
One important idea is contextual advertising.
Instead of saying:
“Show this advertisement to Alok because we know he has visited six technology websites.”
the system says:
“This page is about smartphones, so technology-related advertising may be appropriate.”
That is a profound difference.
The advertisement is selected because of the content being consumed, not necessarily because a company has assembled a long-term behavioural profile of the reader.
Contextual advertising is therefore one of the simplest alternatives to behavioural surveillance.
It also has an important economic advantage:
It does not require knowing the reader’s entire internet history.
First-Party Data Is the Other Big Winner
When third-party tracking becomes harder, information collected directly by a website becomes more valuable.
A newspaper may know that you subscribed.
An online store may know what you bought.
A bank knows what services you use.
A streaming service knows what you watched.
This is first-party data.
Unlike third-party tracking, the relationship is directly between you and the service.
But there is a catch.
First-party does not automatically mean harmless.
A company can collect an enormous amount of information about you inside its own ecosystem.
The internet therefore faces an important transition:
From tracking people across many websites
to
identifying and predicting behaviour inside powerful ecosystems.
That is a very different architecture of surveillance but it can still be surveillance.
The Browser War Is Already Here
There is no single “internet privacy policy”.
Your browser matters enormously.
Safari
Apple’s WebKit blocks third-party cookies by default and uses Intelligent Tracking Prevention (ITP). It also partitions third-party storage and limits several techniques that can be used to recreate cross-site tracking.
Safari has also developed privacy-preserving advertising measurement such as Web AdAttributionKit, designed to measure advertising effectiveness without giving advertisers a conventional user-level identifier.
Firefox
Firefox’s Enhanced Tracking Protection blocks known cross-site tracking cookies, fingerprinters and other tracking content. Its Total Cookie Protection creates a separate cookie “jar” for each website, preventing ordinary cookie sharing from becoming a cross-site identifier.
Firefox also includes additional protection against bounce tracking and fingerprinting.
Chrome
Chrome took a dramatically different route.
Google originally planned to eliminate third-party cookies and replace important advertising functions with Privacy Sandbox technologies.
But in April 2025 Google changed course and decided to maintain its existing approach to third-party-cookie choice rather than introduce a new standalone browser prompt.
The consequence is important:
The third-party-cookie transition is no longer a simple industry-wide switch.
And Google’s own Privacy Sandbox roadmap is changing accordingly. Chrome has begun deprecating several Privacy Sandbox advertising APIs, including Protected Audience and Attribution Reporting, following the decision to maintain its existing third-party-cookie approach.
Why Privacy-Preserving APIs Are Different
The basic philosophy behind technologies such as Apple’s Web AdAttributionKit and Google’s earlier Privacy Sandbox proposals is:
Measure the advertisement without identifying the individual.
That sounds like a small technical adjustment.
It is actually a philosophical change.
Traditional tracking asks:
“Which person clicked?”
A privacy-preserving system tries to answer:
“How many people who saw or clicked this advertisement later converted?”
The second question can still be commercially useful without requiring a permanent identity attached to every event.
Apple’s advertising attribution system, for example, limits the information contained in attribution reports rather than giving advertisers a conventional user or device identifier.
This is the direction privacy engineering is trying to take:
preserve the measurement; reduce the identity.
But Can a New Identifier Become the Old Cookie?
Absolutely.
This is perhaps the most important question in the entire debate.
Suppose the industry stops calling something a “cookie” but begins using:
email addresses;
hashed email addresses;
login IDs;
advertising IDs;
device IDs;
fingerprint-derived identifiers;
server-side identity graphs;
authenticated publisher networks;
probabilistic matching;
cross-device identity systems.
The technical mechanism has changed.
The surveillance objective may not have.
A fingerprint is particularly interesting because it does not necessarily require storing a conventional identifier.
A website can examine combinations of browser and device characteristics and attempt to distinguish one visitor from another.
Firefox explicitly identifies fingerprinting as a technique that can create a unique profile from browser and computer characteristics.
This creates an important privacy test:
Don’t ask only:
“Does this website use cookies?”
Ask:
“Can this company recognise me elsewhere?”
That is the more useful question.
The Advertising Economy Is Too Large to Simply Switch Off
Digital advertising is not a side business.
The IAB/PwC Internet Advertising Revenue Report estimates US digital advertising revenue reached $294.6 billion in 2025, up 13.9% year over year.
That explains why the industry is not abandoning measurement.
The economic incentive remains enormous.
When cross-site tracking becomes harder, several things can happen.
Advertisers
They may lose some precision in audience targeting and attribution.
They increasingly value:
first-party customer information;
authenticated audiences;
contextual targeting;
retail-media networks;
platform-based advertising;
conversion modelling.
Publishers
Large publishers with logged-in users or strong first-party audiences can become more valuable.
Smaller publishers may face greater difficulty proving the value of advertising inventory without reliable measurement.
Ordinary users
Users may see:
fewer conventional retargeted ads;
more contextual advertisements;
more login requests;
more consent banners;
more “personalised experience” prompts;
greater concentration of advertising inside large platforms.
That final possibility deserves attention.
Privacy fragmentation can unintentionally strengthen the companies that already possess large authenticated ecosystems.
The Practical Test: See What Your Browser Knows
You do not need to be a programmer to investigate your own browser.
Chrome: inspect stored website data
Open Chrome.
Go to Settings.
Select Privacy and security.
Open Third-party cookies.
Select See all site data and permissions.
Search for a website.
Inspect the stored data.
Delete individual site data if you no longer want it stored.
Chrome also allows third-party cookies to be blocked globally or permitted for selected websites.
Inspect permissions separately
Go to:
Settings → Privacy and security → Site settings
Here you can review permissions such as:
camera;
microphone;
location;
notifications;
JavaScript-related behaviour;
pop-ups and redirects;
other site capabilities.
Chrome allows permissions to be granted, denied or restricted on a site-by-site basis.
On Android
Open the website, tap the information icon beside the address bar and open Cookies and site data. Chrome allows stored data for that site to be removed from there.
Firefox: Go One Step Further
Firefox gives you a particularly useful privacy inspection route.
Open:
Settings → Privacy & Security
Look at Enhanced Tracking Protection.
Firefox’s default protection blocks known cross-site tracking cookies, while Strict mode goes further. Total Cookie Protection isolates cookies by website.
If you visit a suspicious or heavily commercial website, click the shield icon beside the address bar.
Firefox can show you categories of trackers it has detected or blocked.
That makes the invisible visible.
And that is precisely what good privacy tools should do.
Safari: Check Website Data and Tracking Protection
On Mac, Safari provides:
Safari → Settings → Privacy → Manage Website Data
From there you can inspect and remove stored information for individual websites.
Safari’s Prevent cross-site tracking protection is also central to its privacy model.
WebKit blocks third-party cookies by default and uses additional anti-tracking measures against techniques such as link decoration, script-created storage and CNAME cloaking.
What You Should Actually Do
If your objective is reasonable privacy without breaking the internet, do not start by deleting every cookie.
Use a layered approach.
Keep
essential first-party cookies;
login sessions you trust;
shopping-cart functionality;
necessary site preferences.
Restrict
third-party cookies;
unnecessary cross-site tracking;
excessive browser permissions;
unknown extensions;
unnecessary personalised advertising.
Be particularly cautious about
websites asking for location without an obvious reason;
microphone/camera permissions;
extensions requesting access to every website;
“accept all” consent buttons;
websites requiring unnecessary account creation;
unfamiliar embedded third-party services.
And remember:
Private browsing is not the same thing as anonymous browsing.
A private window mainly limits what is retained locally. It does not magically make the website, your employer, your network provider or every server you contact unable to observe activity.
The New Privacy Question
The old internet privacy question was:
“Does this website use cookies?”
That question is becoming obsolete.
The better questions are:
Who can recognise me?
Where is my identity stored?
Can the same company recognise me on another website?
Can my activity be connected to my real account?
Is tracking occurring locally, server-side or through an intermediary?
Can I delete the identifier?
Can I refuse it without losing access to the service?
Is the system measuring an event—or building a profile?
That last distinction may become the defining privacy question of the next decade.
India’s Privacy Landscape Is Also Changing
For Indian readers, this transition is occurring alongside the implementation of the Digital Personal Data Protection Act, 2023 and the Digital Personal Data Protection Rules, 2025.
The final Rules were notified in November 2025 and establish a phased implementation framework.
This does not mean that every cookie suddenly becomes illegal.
The technology and the legal question are different.
A website can use a cookie for legitimate functionality while a separate tracking system may raise different questions about consent, purpose, disclosure and personal-data processing.
India’s framework therefore makes an important distinction increasingly relevant to ordinary users:
privacy is not simply about whether a file called “cookie” exists on your computer.
It is about what information is collected, why it is collected, how it is processed and what control the individual has.
The Bigger Transition: From Web-Wide Tracking to Ecosystem Surveillance
The most interesting change may not be the disappearance of third-party cookies at all.
It may be the disappearance of the open identity layer that allowed many companies to participate in the same tracking economy.
In its place, we may get a web divided into powerful ecosystems.
Google knows what happens inside Google’s ecosystem.
Meta knows what happens inside Meta’s ecosystem.
Amazon knows what happens inside Amazon’s ecosystem.
A large publisher knows what happens to its subscribers.
Retail-media networks know what customers buy.
And smaller websites may increasingly depend on contextual advertising or relationships with larger platforms.
This creates an uncomfortable paradox.
The web may become harder for dozens of advertising companies to track while becoming easier for a few giant platforms to understand.
That is not necessarily worse.
It is not necessarily better.
It is simply a different architecture of power.
The third-party cookie was never the internet’s only tracking technology.
It was simply one of its most convenient ones.
Its decline has forced the advertising industry to reconsider how targeting, attribution and identity should work.
Some replacements are genuine privacy improvements:
contextual advertising;
partitioned storage;
privacy-preserving attribution;
aggregated measurement;
browser-level protections.
Others can recreate much of the old problem:
fingerprinting;
cross-site identity graphs;
authenticated tracking;
device matching;
server-side identifiers;
aggressive first-party data collection.
So when you hear “the cookie is dead,” don’t celebrate too quickly.
Ask the more useful question:
If the cookie disappeared tomorrow, what would still allow a company to recognise me?
That is where the future of online privacy is actually being decided.
Key Unfoldings
| Question | Reality |
| Are third-party cookies the same as all cookies? | No |
| Does blocking them stop all tracking? | No |
| Can websites still track without cookies? | Yes |
| Is fingerprinting an alternative? | Yes |
| Is first-party data automatically private? | No |
| Is contextual advertising less dependent on personal tracking? | Generally yes |
| Can advertising work without identifying individuals? | Increasingly, yes |
| Does browser choice matter? | A great deal |
| Is Chrome eliminating third-party cookies? | Not under its current 2025 approach |
| Does “cookie-free” mean “private”? | Absolutely not |
What readers should do today
1. Check your browser’s stored site data.
2. Block or restrict third-party cookies where practical.
3. Review camera, microphone and location permissions.
4. Remove extensions that have unnecessary access to every website.
5. Prefer contextual advertising and privacy-preserving measurement over behavioural profiling.
6. Remember that being logged in can itself create a powerful identifier.
7. Judge a website by what it can learn about you—not merely by whether it uses cookies.
FAQs
Are first-party cookies safe?
Not automatically. They are usually necessary for functions such as login, preferences and shopping carts, but the website itself can still use first-party information for analytics, personalisation or advertising.
Can fingerprinting identify me without cookies?
It can potentially distinguish your browser or device using a combination of technical characteristics. Fingerprinting is therefore one reason blocking cookies alone does not solve online tracking.
Which browser is most private?
There is no single answer for every user. Safari and Firefox currently implement strong built-in restrictions against cross-site tracking, while Chrome provides extensive user controls but has taken a different policy approach to third-party cookies.
Does deleting cookies stop companies from knowing who I am?
No. If you are logged into an account, the service may already know your identity. Server-side records, fingerprints, first-party data and other identifiers can also remain relevant.
Does Incognito make me anonymous?
No. It mainly reduces local browser storage and history. It should not be treated as an anonymity system.
Why do advertisers need tracking?
Advertising businesses want to determine which audiences are likely to respond to an advertisement and whether advertising generated a result. Privacy-preserving systems attempt to provide useful measurement without exposing a persistent individual identity.
Source Notes and Further Reading
- Mozilla — Firefox Enhanced Tracking Protection and Total Cookie Protection.
- WebKit — Tracking Prevention and Intelligent Tracking Prevention.
- Google Chrome — Current third-party-cookie controls.
- Google Privacy Sandbox — April 2025 change in Chrome’s third-party-cookie approach.
- UK Competition and Markets Authority — Privacy Sandbox investigation and 2025 decision.
- MDN Web Docs — Third-party cookies and cross-site tracking.
- UK Information Commissioner’s Office — 2026 guidance covering cookies, pixels, fingerprinting, scripts and link decoration.
- US Federal Trade Commission — How websites and apps collect and use information.
- IAB/PwC — 2025 Internet Advertising Revenue Report.
- Apple/WebKit — Privacy-preserving advertising measurement and Web AdAttributionKit.
- Government of India, MeitY — Digital Personal Data Protection Act and Rules 2025.
- Government of India, Department of Consumer Affairs — consumer protection and dark-pattern resources.
Leave a Reply